
AppSec expertise. Put to work.
A Positive Change for Our Industry
DryRun Security Co-founders James Wickett and Ken Johnson have created a guide for a new approach to DevSecOps: Contextual Security Analysis (CSA).
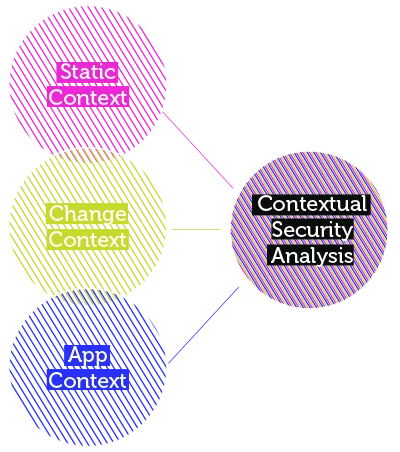
CSA layers static context, change context, and app context to make contextually aware assertions in near real-time and is ideal for modern applications, which are often distributed, microservices-based, and rely heavily on APIs and third-party components.
CSA is an approach that:
- fits naturally in an organization practicing DevOps
- prioritizes reducing security tool pressure on developers
- makes it easy for developers to reason about security
Download the guide to find out more about how to:
- find context using the SLIDE model
- reduce sectool pressure on the CI/CD pipeline
- provide collaboration between developers and security
AppSec expertise. Put to work.
Key Benefits of Contextual Security Analysis Guide
Better decision-making
Prioritize protecting sensitive data and services, identify potential vulnerabilities, and evaluate the security implications of changes to the application.
Improved collaboration
Foster a culture of shared responsibility for security by encouraging developers and security teams to share knowledge and insights about the application's context.
Greater agility
Quickly assess the security implications of changes to the application, allowing them to iterate and innovate more rapidly.
Increased visibility
Move from the binary view of secure or not secure and have a visual representation of how changes impact the system from routing and codepaths to functions and syntax.
AppSec expertise. Put to work.
Written by AppSec practitioners
James Wickett
Co-founder & CEO, DryRun Security
Ken Johnson
Co-founder & CTO, DryRun Security